
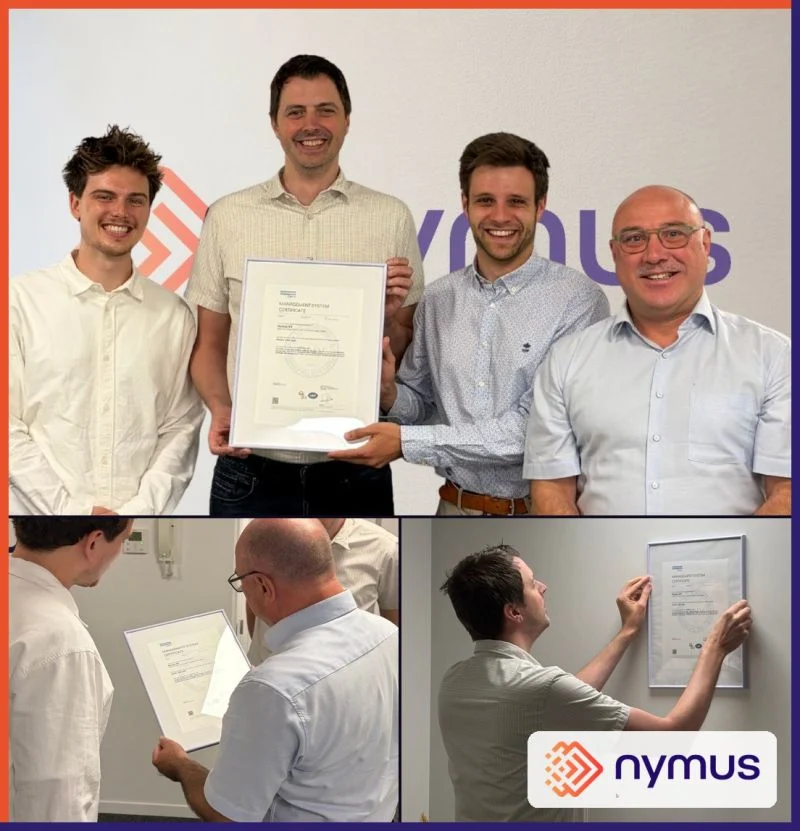
Why Nymus took this step
As an e-invoicing partner, Nymus processes information that is important to its customers’ day-to-day operations. Demonstrable information security therefore plays a key role in customer trust.
Nymus deliberately chose certification as part of its growth strategy. Larger companies set security requirements for their suppliers, and the ambition to grow internationally, including in the Netherlands, made a recognised framework all the more relevant.
What certification demonstrates
ISO/IEC 27001 sets out the requirements for an information security management system, or ISMS. Such a system helps an organisation assess risks, choose appropriate measures and keep improving how well they work. It covers people, processes and technology.
For Nymus, the certificate provides independent confirmation of its management system within the assessed scope. Customers can use this in their supplier assessments. The certificate builds trust; maintaining the system is an ongoing task.
Guidance and independent certification
Cyberwise guided Nymus towards certification. The certification audit and the award of the certificate were handled by DNV. This keeps guidance clearly separate from the independent assessment by the certification body.
What your organisation can learn from this
This case shows how information security can support commercial ambitions and customer expectations. Thinking about ISO/IEC 27001 yourself? Start by clarifying which activities and information you want to protect, what customers expect and where your main risks lie.
From there, you can set priorities, assign responsibilities and build a workable ISMS. The real value lies in day-to-day application and follow-up. Certification can then provide independent confirmation of that work.